SpencerWeb
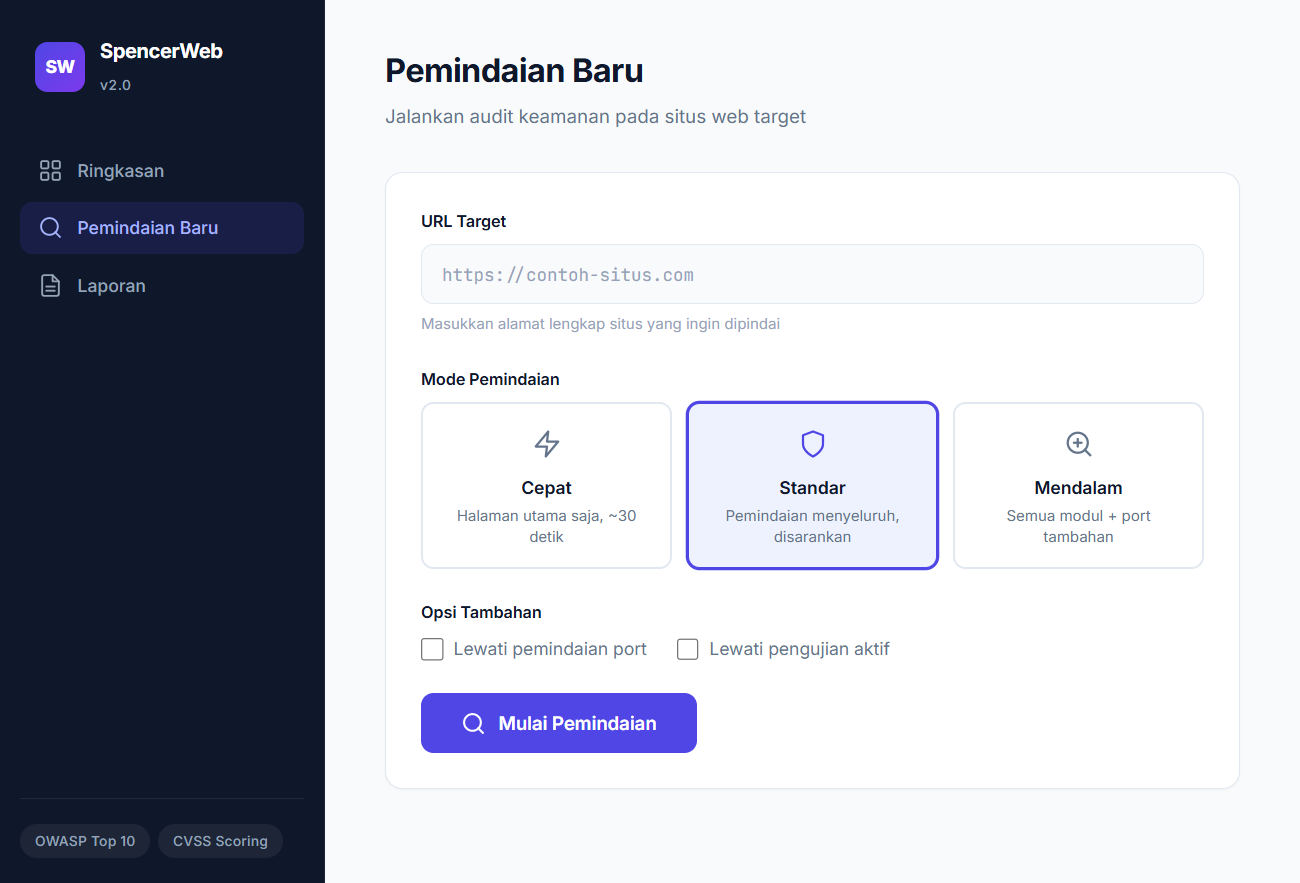
Web vulnerability scanner covering SQLi, XSS, CSRF, SSL issues, open ports, and exposed files, mapped to the OWASP Top 10. Ships a live dashboard and auto-generated PDF reports. Built as my final project.
the problem
Small businesses and student projects rarely get a real security audit before going live -- commercial scanners are expensive or built for enterprise teams, and free tools tend to flood a report with false positives instead of ranked, actionable findings.
approach
Built as my Computer Engineering final project (TA, Politeknik Negeri Medan), SpencerWeb runs 10 scanning modules end to end: a crawler maps the site and every form first, then passive checks (headers, SSL/TLS, exposed files, CMS/plugin fingerprinting) run alongside active checks (SQL injection with error/boolean/time-based detection, reflected and stored XSS, CSRF token analysis, port reconnaissance). Findings map directly to OWASP Top 10 categories and get scored with CVSS, then compiled into a client-ready PDF.
architecture
CLI scanner (Python)
10 modules from deep crawl through active exploitation checks, runnable standalone for CI or headless audits.
Web dashboard (Node/Express)
Real-time scan progress, historical scan comparison, and a visual report -- the same engine, a UI on top.
PDF reporting (ReportLab)
Auto-generates a professional, partner-ready report from the same scan data the dashboard shows live.
SQL injection module
The one module explicitly marked "verified" in its own docs: error-based, boolean-based, and time-based detection, not just pattern matching on response text.