Scepter
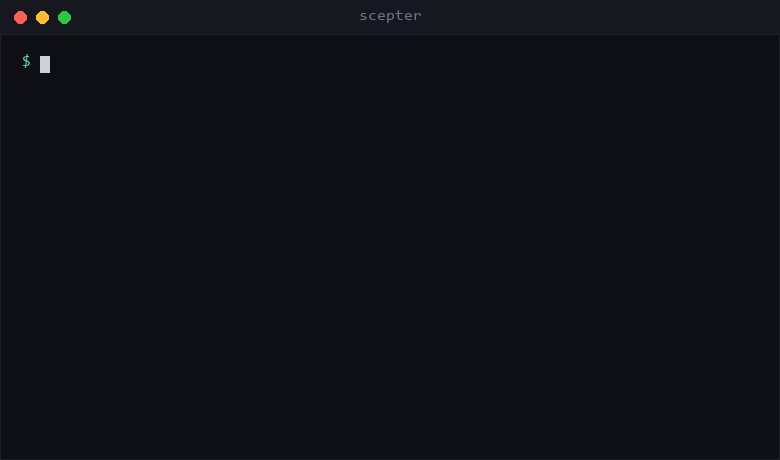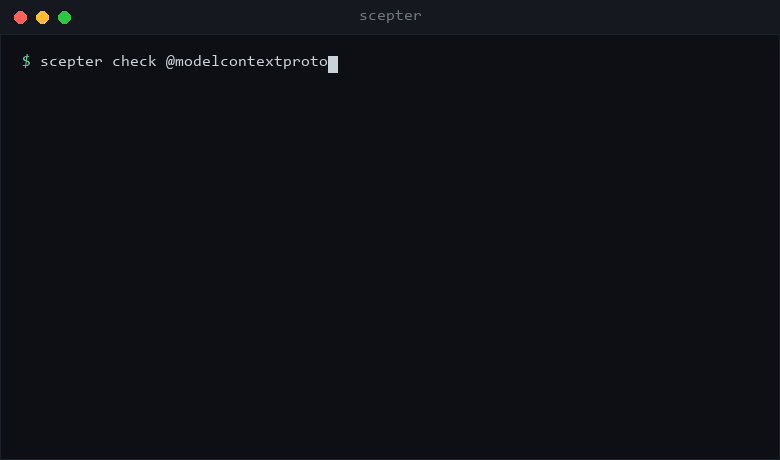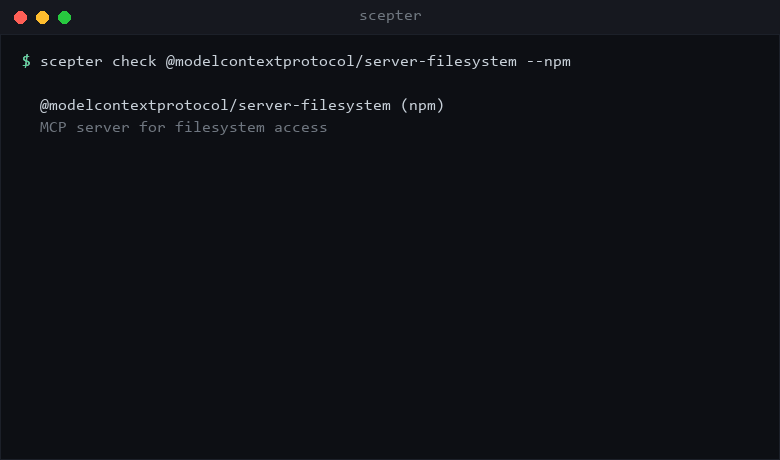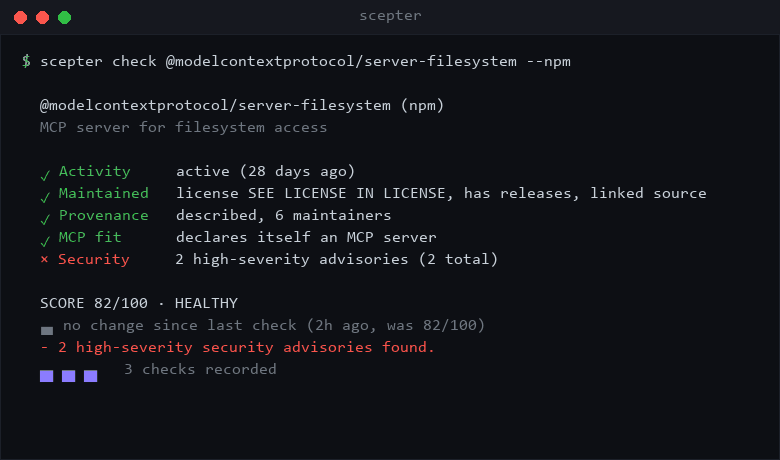
Zero-dependency CLI that checks whether an MCP server is alive, maintained, and safe before you wire it into an agent. Runs health, wrap, report, and badge commands. Published on npm as scepter-mcp.
the problem
More than half of published MCP servers are already dead or unmaintained, and agent builders wire them into production without any way to check. There was no single command that answered "is this safe to depend on?"
approach
Scepter reads registry and repository metadata (npm + GitHub) and scores a server on four signals, with zero runtime dependencies so it stays fast to install via npx. Beyond the static check, a wrap mode sits between an agent and the real MCP server as a transparent proxy: every tool call, its result, timing, and any error gets logged locally, so a developer can see how a server actually behaves in production, not just what its README claims.
architecture
Health scoring
Four signals -- activity (last publish/push), maintained (archived flag, license, releases), provenance (stars, maintainers, issues), and MCP fit -- combined into a single score with a healthy/caution/risky verdict.
Proxy wrap
scepter wrap sits in the MCP client config in place of the real server, forwards every byte unchanged, and records call-level telemetry to ~/.scepter. Nothing leaves the machine.
CI-friendly exit codes
Exit code 1 on a risky verdict, so scepter check can gate a CI pipeline before a risky server gets deployed.
Badge generation
scepter badge prints a copy-paste Markdown health badge for a project README, sourced from the same live score.